NGINX Warns About Serious HTTP2 Security Flaws
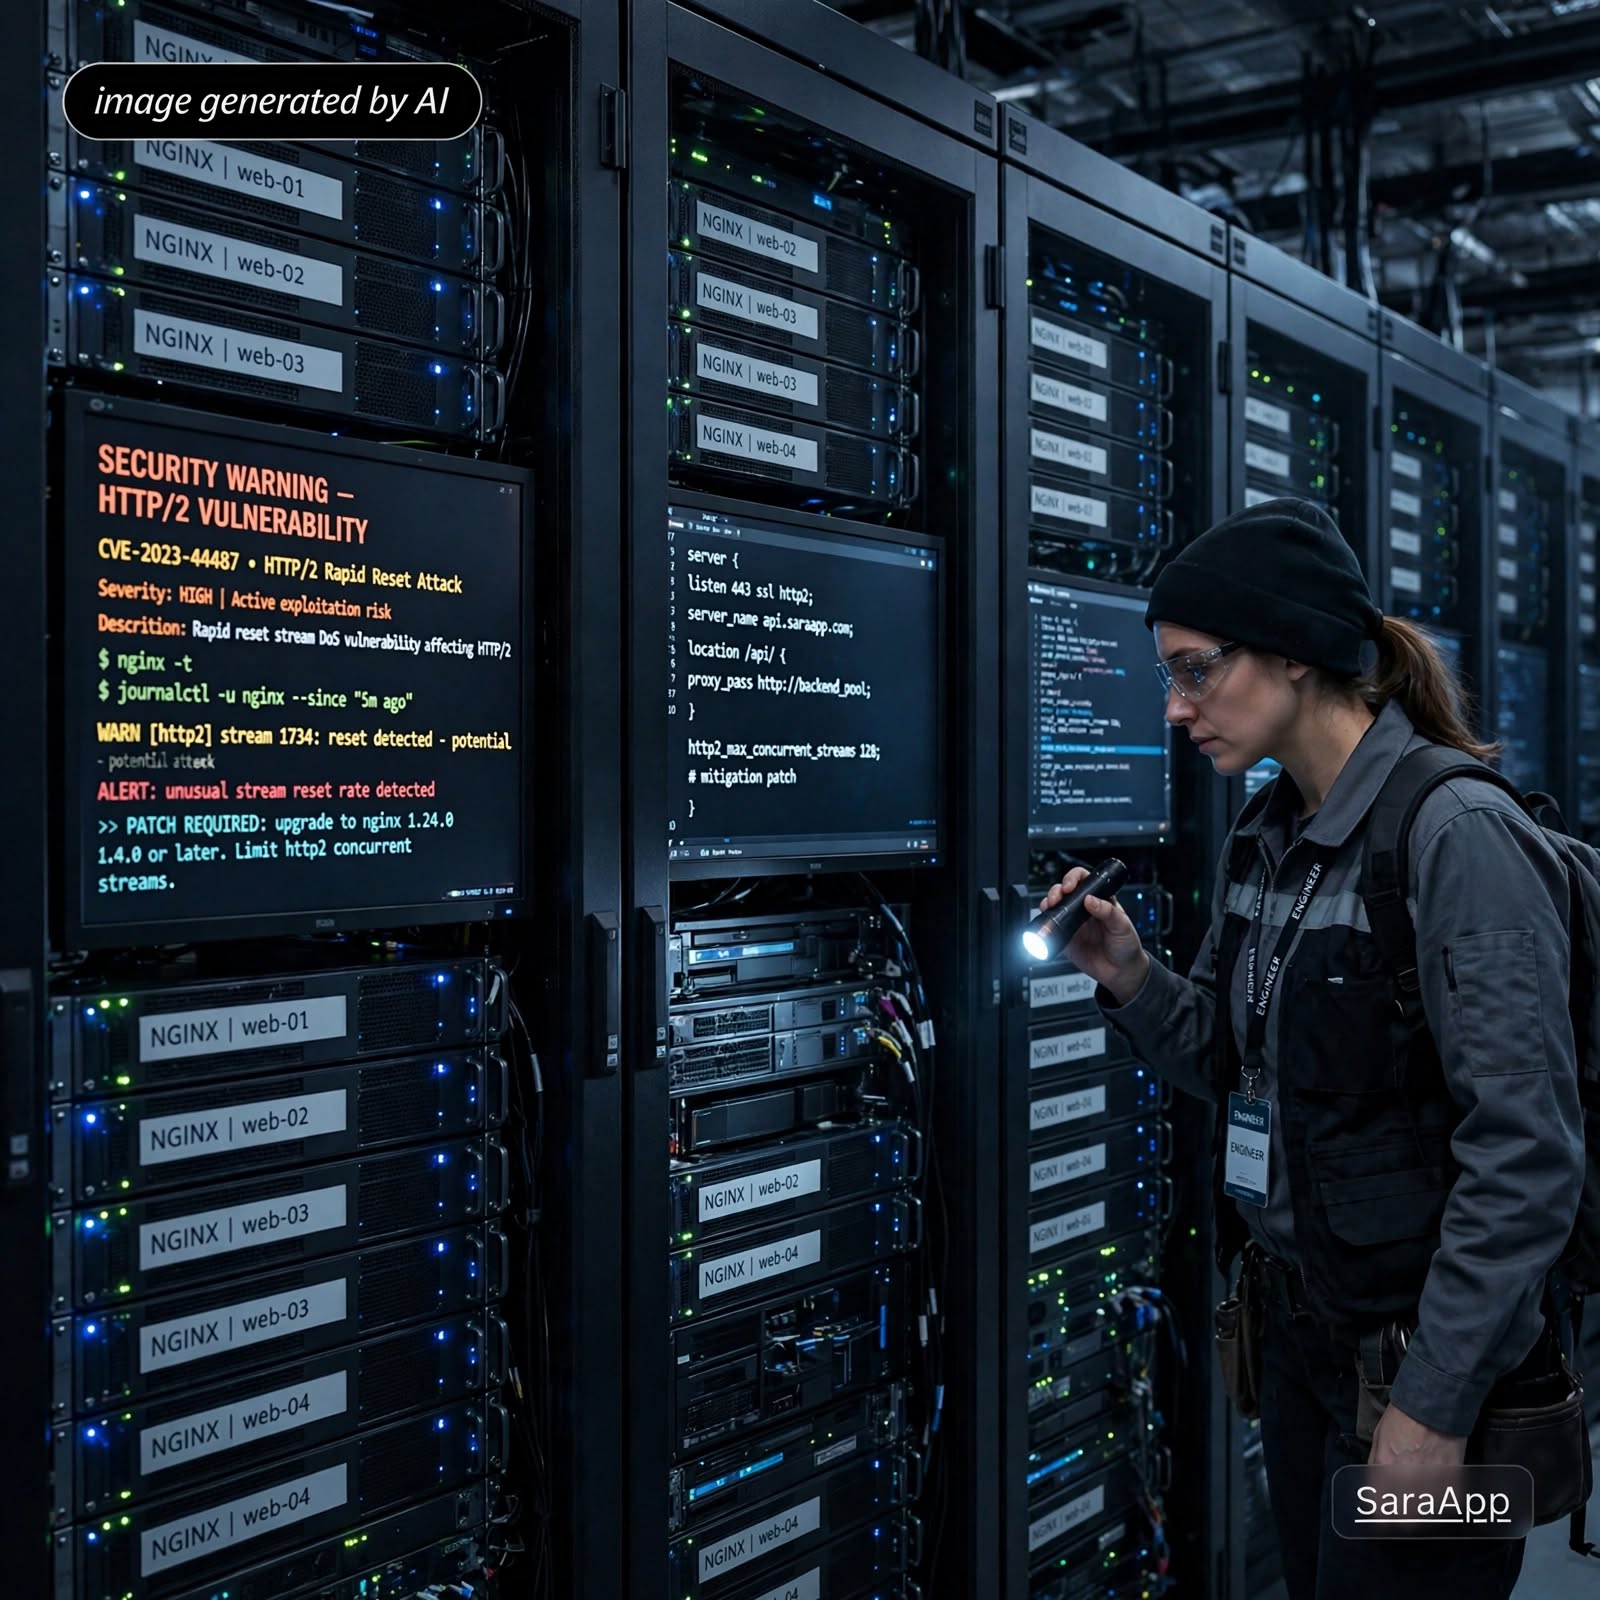
A serious security warning about NGINX has become one of the most searched technology topics today. Researchers revealed unauthenticated remote code execution flaws in NGINX linked to HTTP2, with reference codes CVE-2026-123633 and CVE-2026-123007. The flaws could allow an attacker without any login to run malicious code on a vulnerable server if the system is not updated. NGINX powers a huge share of websites, content delivery networks and cloud services around the world, so the warning has drawn attention from developers and security teams. Experts urge administrators to check their NGINX version, apply the latest patches and review their HTTP2 settings as soon as possible. Companies should also check logs for unusual activity and make sure their monitoring tools are active. The discovery shows how important it is to keep web server software updated, even when systems appear to be working normally. Security teams are now sharing guidance and best practices to help organisations protect their servers. For users, the key message is simple and clear. Keep systems updated and follow official security advice.